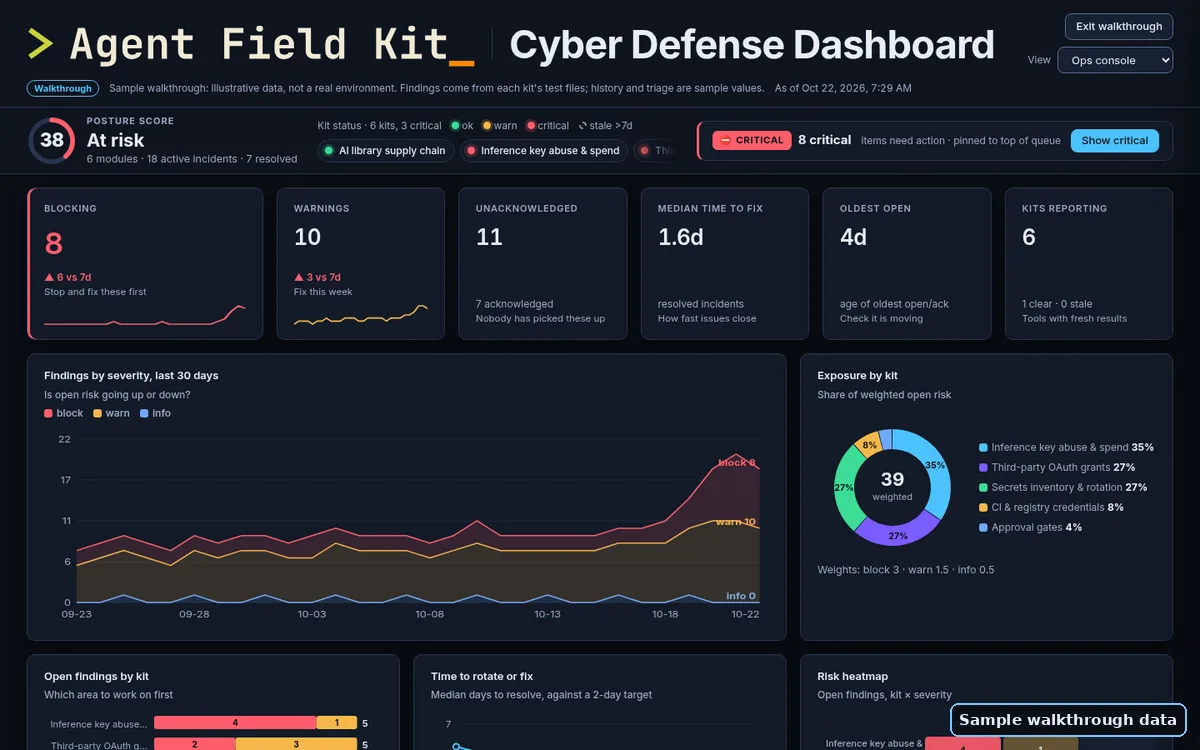
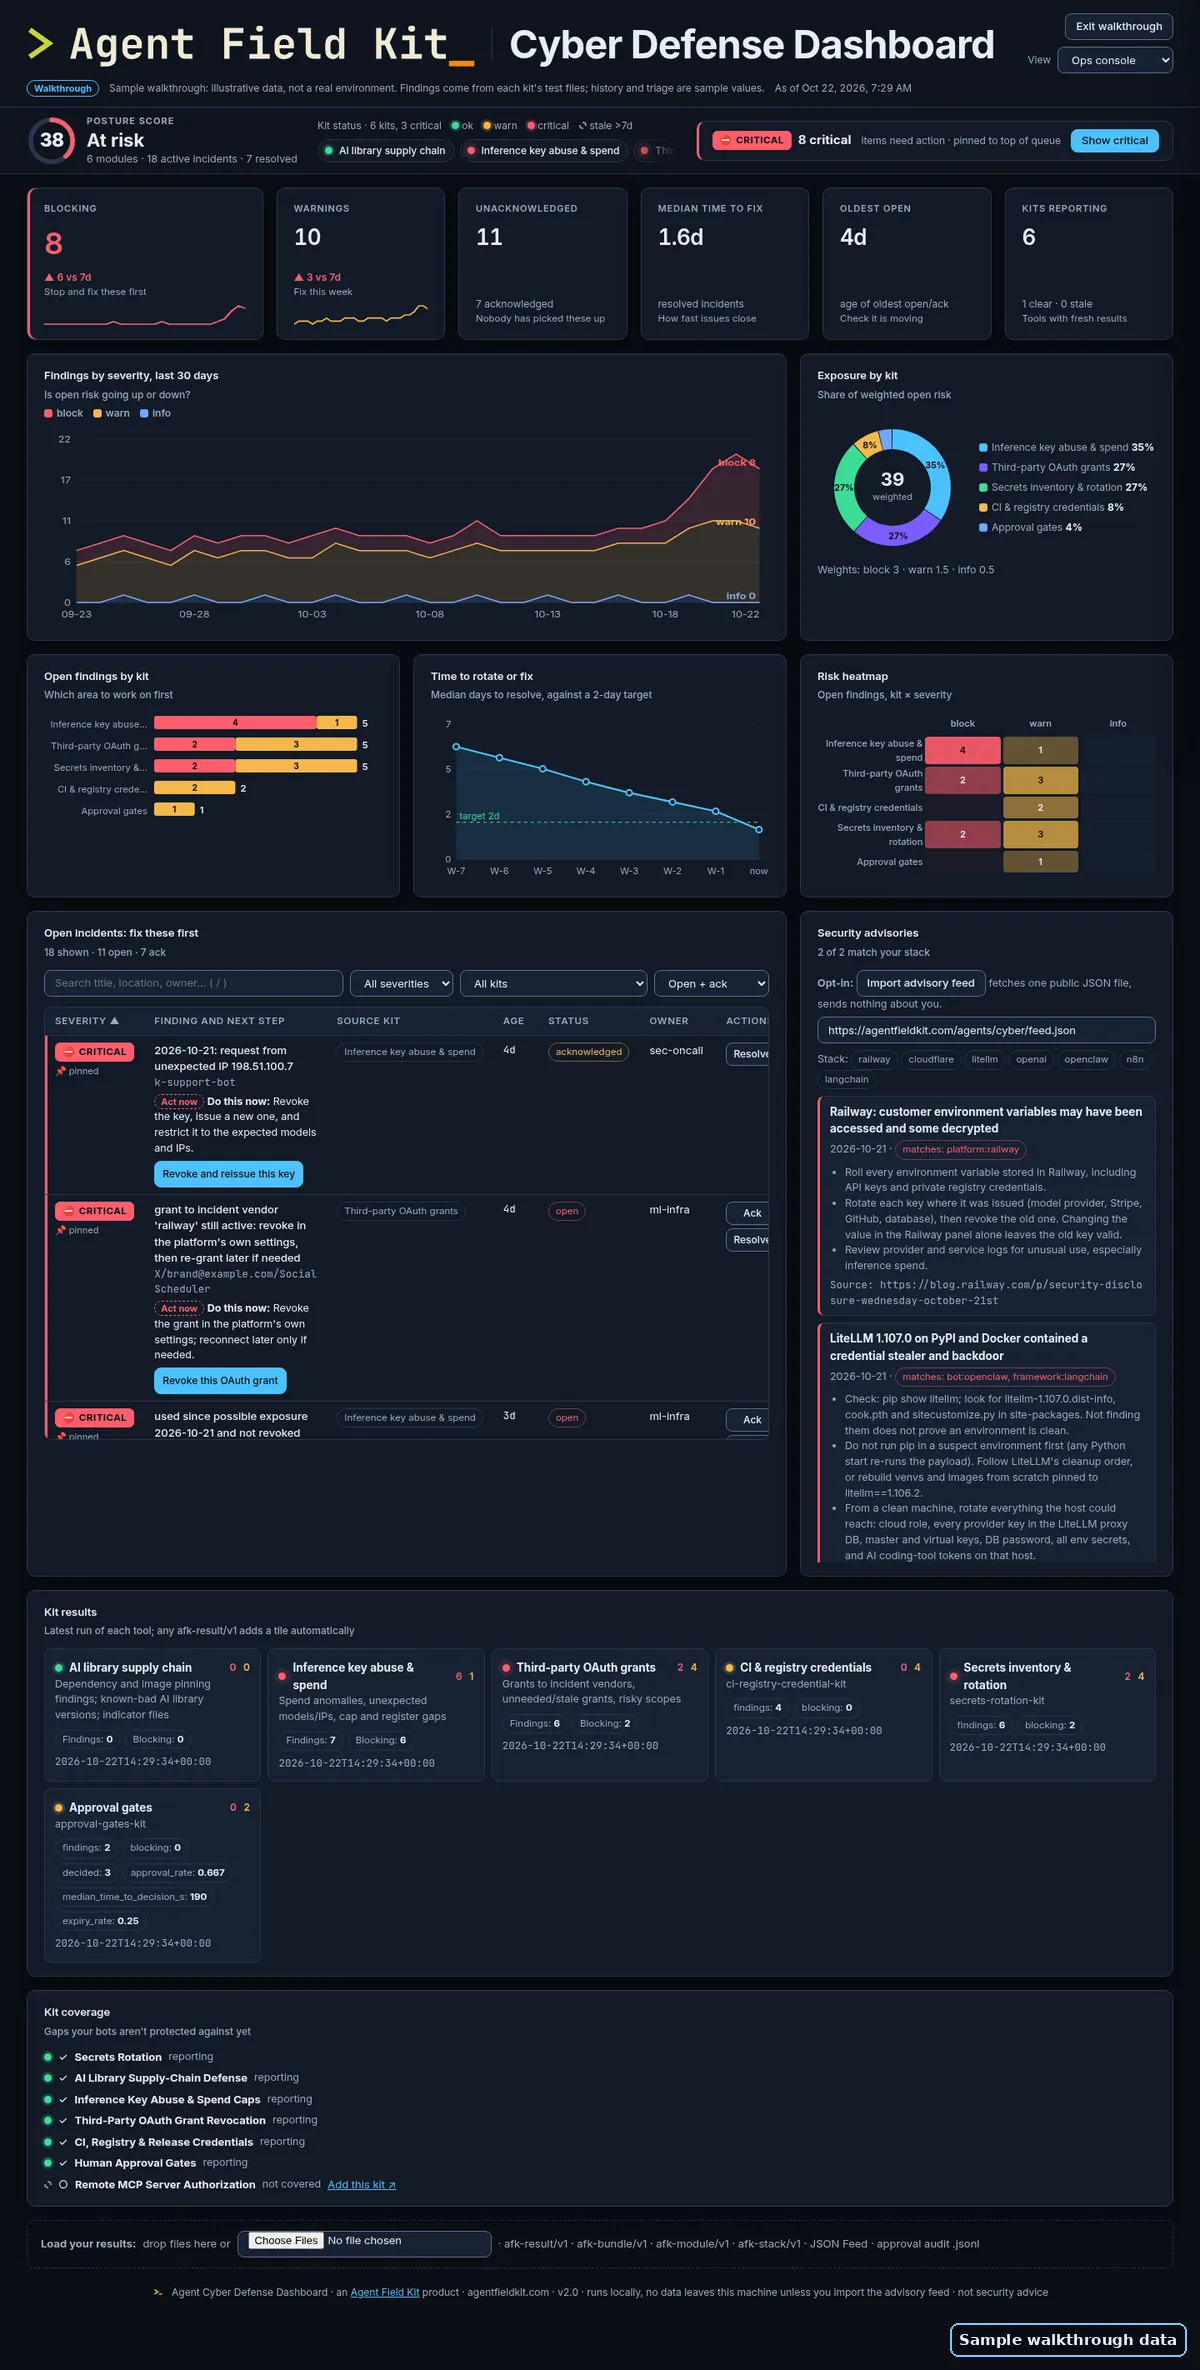
HTML / JSON schema / Python script (ZIP + PDF)One self-hostable, local-only HTML dashboard (no network calls by default) that unifies every Agent Field Kit cyber tool: secrets rotation status, AI-library supply-chain findings, inference spend anomalies, OAuth grants, CI and registry credential findings, approval-gate metrics, and advisories matched to your stack. Tools emit a shared afk-result/v1 JSON plus an optional module manifest, so new kits, tools and newly emerging attacks plug in without changing the dashboard. Optional opt-in import of the free AFK advisory feed. New in v12: a stack exposure check (exposure_check.py matches your package and runtime versions against known affected and fixed versions; bundled data works offline, OSV.dev and CISA KEV lookups are opt-in), a patch status on every finding (no fix yet, mitigation only, patched with the fixed version) with a matching next step, and a "days since last incident" view per stack. Includes afk_adapt.py (adapters, validator, bundler) and a sample-walkthrough build (real kit tool output on built-in test files).
What's inside
dashboard.htmldashboard.template.html01_Dashboard_Guide.mdschema.mdafk_adapt.pybuild_demo.pystack.example.jsonsamples/release.ymlexposure_check.pyexposure.module.jsonadvisory_intel.jsonsamples/stack.versions.json20_Agent_Cyber_Defense_Dashboard.pdf: every document in one printable guide
Verify it works
python3 afk_adapt.py --selftestandpython3 build_demo.py --selftestprintselftest ok.- Open
dashboard.htmlin a browser and click Load sample walkthrough: the console switches to a labelled walkthrough mode showing real output of each kit tool run against its built-in test files (module tiles, a findings table sorted by severity, metrics cards, and advisories from the feed matched to the test stack). No history or trend data is invented; those charts stay empty until you record your own runs. - Confirm it is local-only: open the browser's network tab, reload, and see no requests (until you click Import advisory feed).
- Run your kit tools with
--afk-json(see 01), runpython3 afk_adapt.py validate results/*.json, then load your files. Python 3.9+ and any modern browser, no installs.
Preview
First part of the main document, shown as-is:
Agent Cyber Defense Dashboard: guide
One local HTML file that shows every Agent Field Kit cyber tool's results in one place: secrets rotation status, AI-library supply-chain findings, inference spend anomalies, OAuth grants, CI and registry credential findings, approval-gate metrics, and advisories matched to your stack.
Privacy model
dashboard.htmlis self-contained. Open it from disk or serve it behind your own auth. It makes no network calls unless you click Import advisory feed, which fetches one public JSON file (defaulthttps://agentfieldkit.com/agents/cyber/feed.json, sent without cookies or a referrer). A Content-Security-Policy tag blocks every other origin.- Files you load are read in the browser and never uploaded.
Daily or weekly routine (10 minutes)
mkdir -p results
python3 supply_chain_check.py ./ --afk-json            > results/supply-chain.json
python3 key_abuse_check.py usage.csv --register key_register.csv --afk-json > results/inference-keys.json
python3 ci_credential_check.py .github/workflows --afk-json > results/ci-credentials.json
python3 oauth_grant_check.py grants_register.csv --afk-json > results/oauth-grants.json
python3 rotation_check.py secrets_inventory.csv --json > raw-rot.json && python3 afk_adapt.py rotation raw-rot.json > results/secrets.json
python3 audit_report.py audit.jsonl --json > raw-ag.json && python3 afk_adapt.py approvals raw-ag.json > results/approvals.json
python3 afk_adapt.py validate results/*.json
python3 afk_adapt.py bundle results/*.json stack.json > bundle.json   # optional: one file to load
Then open dashboard.html and load the files (or bundle.json). An approval-gate audit log (.jsonl) can also be dropped in directly. The approval metrics reuse the Approval Gates kit's review-surface patterns.
Matching advisories to your stack
Copy stack.example.json and list your platforms, packages, bots and frameworks. Advisories in the AFK feed carry _afk.affected and _afk.components (for example platform:railway, package:litellm). The dashboard highlights matches and lists the free actions from each advisory with its primary source.