Doc / CSV / Python script (ZIP + PDF)When a vendor that holds tokens to your accounts may be breached (as with apps hosted on Railway on Oct 21), revoking its access at each platform is the step that works even while the vendor is down. This kit gives an Oct 21 response section, where-to-revoke steps for GitHub, Google, Microsoft, Slack, X and LinkedIn, a grant register, a quarterly review routine, and oauth_grant_check.py, which flags grants to an incident vendor, unneeded or stale grants and high-risk scopes. Includes a per-bot guide (Grok Bot, OpenClaw, ChatGPT, Claude, Cursor, n8n, Manus; Instinct, Muse and Dot marked unverified). v2: --afk-json output and module.json plug into the Agent Cyber Defense Dashboard.
What's inside
01_Oct21_Vendor_Token_Response.md02_Where_To_Revoke.md03_Per_Bot_Guide.md04_MCP_Server_Grants.mdgrants_register.csvoauth_grant_check.pymodule.json19_OAuth_Grant_Revocation_Kit.pdf: every document in one printable guide
Verify it works
python3 oauth_grant_check.py --selftestprintsselftest ok.python3 oauth_grant_check.py grants_register.csv --incident-vendor railway --today 2026-10-22flags the example grant to a Railway-hosted app and exits 1.- List your own grants from each platform's connected-apps page (02). Names and scopes only.
- Revoke, fill
revoked_on, re-run until it exits 0. - Dashboard: add
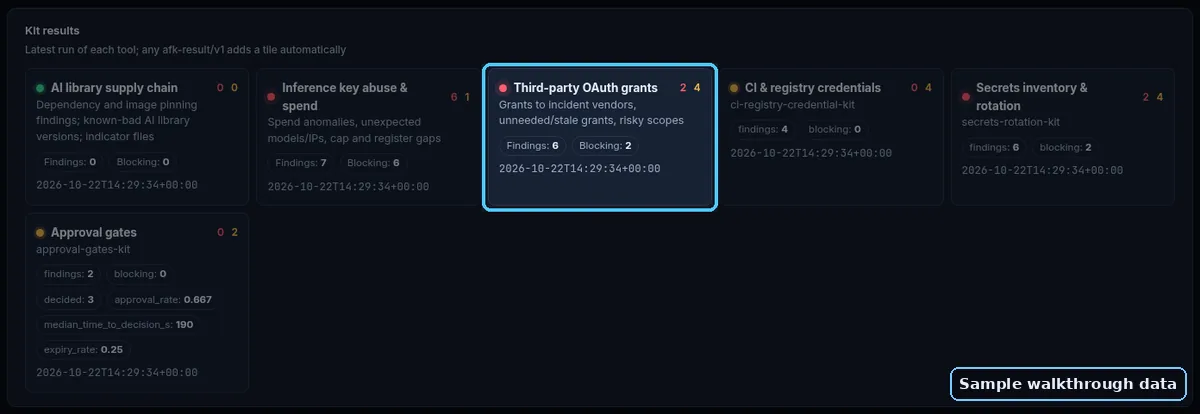
--afk-jsonto any command above and save the output asresults/oauth-grants.json; load it in the Agent Cyber Defense Dashboard. Python 3.9+, no installs. Read-only: nothing is changed, sent or uploaded.
Oct 2026 update (section 04)
- [ ] MCP server connections listed in every coding agent and added to the register.
- [ ] Unrecognized servers removed and their OAuth grants revoked at the identity provider.
Preview
First part of the main document, shown as-is:
Oct 21 incident response: third-party app tokens
Facts we rely on (Oct 21, 2026; wording follows the sources)
- Railway says an unauthorized party may have accessed encrypted environment variables and, for some, obtained decrypted contents. It believes this is part of a series of attacks targeting platform companies to compromise AI inference providers, and notified upstream providers to revoke keys. It recommends all users roll every variable and private registry credential and review logs. (https://blog.railway.com/p/security-disclosure-wednesday-october-21st)
- Railway later reset bucket S3 credentials and the GitHub tokens it held, and invalidated all Railway API tokens. GitHub tokens stored as registry credentials still work on GitHub until you revoke them. (https://blog.railway.com/p/security-disclosure-recommendation-redeploy-buckets-and-reconnect-github-after-the-credential-reset, https://status.railway.com/incident/QH8L8B3E)
- Railway published provider-specific guides to check for unexpected Anthropic and xAI (Grok) usage. (https://blog.railway.com/p/security-disclosure-recommendation-check-for-unexpected-anthropic-usage, https://blog.railway.com/p/security-disclosure-recommendation-check-for-unexpected-grok-usage)
- LiteLLM says its release pipeline was compromised and
litellm==1.107.0(PyPI, 11:39-13:23 UTC) plus Docker/GHCR tagsv1.107.0,latest,main-latest,main-stable(from 11:46 UTC) contained credential-stealing malware. The attacker used leaked developer GitHub CLI OAuth tokens found in logs of an internal deployment. (https://docs.litellm.ai/blog/security-incident-oct-21-2026, https://osv.dev/vulnerability/MAL-2026-2144)
Who this is for
You connected accounts (GitHub, Google, Slack, X, LinkedIn, Microsoft) to a tool that runs on Railway, to a tool that ran litellm 1.107.0, or to Railway itself. Railway's disclosure covers secrets stored in environment variables; whether a given vendor kept user tokens there is something to ask that vendor. Revoke as a precaution.
Steps
- List vendors at risk: tools you know are hosted on Railway or use LiteLLM, plus Railway's own GitHub connection. Ask each vendor to confirm; don't wait for the answer to revoke.
- Revoke at the platform (02), not inside the vendor's app. This works even if the vendor is offline.
- Check activity on each account from Oct 21: posts, DMs, emails, repo pushes, new deploy keys, forwarding rules, new OAuth apps.
- Re-grant only when needed, with the narrowest scopes, after the vendor confirms it has rotated its own secrets.
- For GitHub: reconnect Railway's GitHub integration per Railway's guide and revoke any PATs you stored there. (https://blog.railway.com/p/security-disclosure-recommendation-redeploy-buckets-and-reconnect-github-after-the-credential-reset)
- Record each revocation in
grants_register.csv.